Operations | Monitoring | ITSM | DevOps | Cloud

The latest News and Information on Log Management, Log Analytics and related technologies.

solr-reindexer: Quick Way to Reindex to a New Collection

If you’re using Solr, for sure there are times when you change the schema and need to reindex. Quite often the source of truth is a database, so you can use streaming expressions via the JDBC source to reindex. But sometimes that’s not possible or adds too much load to the DB. So how can we use Solr itself as a source?
Welcome to the Future of Data Search & Exploration

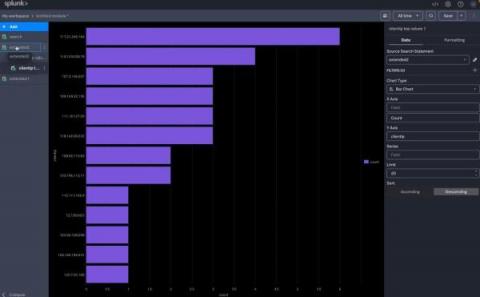
You have more data coming at you than ever before. Over the next five years, the total amount of digital data is going to be more than twice the amount of data created since the advent of digital storage. With the success of your company often determined by how you anticipate and respond to threats – and leverage meaningful insights – you need the ability to quickly search and find insights in your data, despite this increasing deluge of information.

Network as Code Explained: How Ansible & Automation Support Agile Infrastructure

When considering application source code, the way you maintain consistency throughout environments is mostly straightforward. You write application code, commit it to source control, and then build, test and deploy via a CI/CD pipeline. Since the application is defined by the source code living in source control, the build will be identical in all environments to which it’s deployed. But what about the infrastructure on which an application runs?

Exporting Splunk Data at Scale: See a Need, Fill a Need

The Core Splunk platform is rightfully recognized as having sparked the log analytics revolution when viewed through the lenses of ingest, search speed, scale, and usability. Their original approach leveraged a MapReduce approach, and it still stores the ingested data on disk in a collection of flat files organized as “buckets.” These immutable buckets are not human-readable and largely consist of the original raw data, indexes (.tsidx files), and a bit of metadata.

Introducing instant Kubernetes logging with Kubernetes Monitoring in Grafana Cloud

Kubernetes, Prometheus, and Grafana are a trio of technologies that have transformed cloud native development. However, despite how powerful these three technologies are, developers still face gaps in the process of implementing a mature Kubernetes environment.

Driving Innovation Aligned with the AWS Security Competency Re-launch

Logz.io recently obtained the Amazon Web Services (AWS) Security Competency for our Cloud SIEM. We are thrilled to support the re-launch of the AWS Security Competency, as clearly the only way to combat today’s cybersecurity challenges is to modernize your analytics platform to respond to today’s evolving threat landscape.

How to monitor Jetty using OpenTelemetry

You can now monitor Jetty for free using top of the line open source monitoring tools in OpenTelemetry. If you are as excited as we are, take a look at the details of this support in OpenTelemetry’s repo. The best part is that this receiver works with any OpenTelemetry collector: including the OpenTelemetry Collector and observIQ’s distribution of the collector. Jetty uses the JMX receiver.

Masking PII: Minimize Your Risk and Stay Out of Trouble

Consumers expect their personal information to be safe in your hands as they use your apps, services, and stores. Even in-person retailers collect customer data for loyalty programs, shopping history, and more. In addition, regulators and auditors — and while we’re at it, let’s add investors, board members, and partners to the list of people who expect all customer data to be secure at all times.