Operations | Monitoring | ITSM | DevOps | Cloud

The latest News and Information on CyberSecurity for Applications, Services and Infrastructure, and related technologies.

What Is SOC 2 Compliance? Requirements, Controls, and Evidence

Your largest prospect has asked for your SOC 2 report. The deal sits still until you produce one. Most teams handle the first half of SOC 2 compliance fine. They control access. They run backups. They put changes through approval before anything ships. The second half is what stops them, and that half is proof. Your policy says access gets reviewed every quarter. The auditor wants the dated review, the signature on it, and the same record from eight months ago.

How to Secure Cisco AnyConnect, Fortinet, and Palo Alto VPNs with RADIUS MFA

VPN is the first thing attackers test when they're trying to get inside a network. Not because VPN is technically weak - it's not - but because it's the front door, it's usually internet-facing, and in most organizations it asks for exactly one thing: a username and a password.

Vulnerability Assessment and Penetration Testing: Differences, Cadence, and Cost

What do you say when an auditor asks for evidence that your security controls hold, and all you can produce is a scan report from last month? A scan lists weaknesses. It says nothing about whether an attacker could chain three of them together and reach the customer database. Vulnerability assessment and penetration testing answer two different questions about the same environment. The first asks what is exposed right now. The second asks what someone with intent and skill could do with that exposure.

What Is the MITRE ATT&CK Framework? A Guide for IT Ops Teams

Most IT operations teams cannot say how much of the MITRE ATT&CK framework they already cover. The framework gets explained in the language of threat hunting and red teams. The parts that belong to infrastructure work are easy to miss. And then, coverage questions get answered with a guess. The mismatch costs time on both sides. Security asks for a coverage answer that ops has no clean way to produce. Yet the controls that stop a large share of those techniques already sit with your team.

Why QKD Is Gaining Attention in Critical Infrastructure Security

A power supply company has planned a renovation. Well, replacing the office furniture and appliances is not a hassle, but then changing the cryptography embedded in substations, control centers, field gateways, and decade-old operational technology requires different planning and execution. In most cases, these systems have been in service long after encryption protecting them has become questionable.

7 Business Messages That Need More Than a Send Confirmation

Some business messages carry legal or financial weight, and knowing that the email left your outbox tells you very little about whether that weight actually landed. Delivery receipts confirm that a server accepted the message, which falls a long way short of confirming that the right person received it, opened it, or got hold of it inside the window a contract or a statute allows. When a disagreement surfaces eighteen months later, nobody asks whether you meant to send something. They ask what you can show about when it went out and who took it in.

Why Responsible Technology Use Matters

Technology plays an integral role in our lives today. Technology is applied in communications, education, business, shopping, and various other tasks we undertake daily. The emergence of new forms of technology such as Artificial Intelligence, Cloud Computing, and IoT has made life more comfortable, but at the same time, they present challenges including privacy concerns, cyberattacks, and the spread of misinformation, among others.

What Is a Vulnerability Scan? How It Works and What the Results Mean

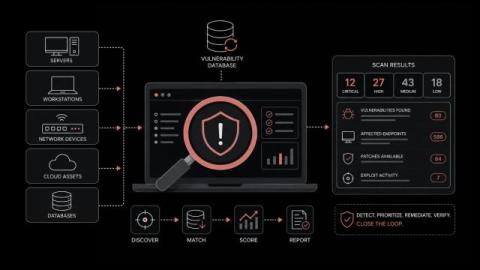
How many machines in your environment are running software with a publicly documented security flaw right now? That figure comes from an asset inventory, and asset records age quickly once they are written. The gap is rarely about tooling budgets. Software inventory across a few hundred endpoints shifts every week, while the published catalogue of flaws in that software grows every single day. Manual inspection loses that race inside the first month.

Ensuring Policies Are Read and Understood: The Power of True Policy Acknowledgment

Simply emailing a PDF or storing a document in a shared folder does not mean your team has actually read or understood it. True policy acknowledgment requires an active, trackable process that proves employees have received, reviewed, and agreed to critical corporate guidelines. Without measurable verification, organizations face significant compliance risks, audit failures, and operational gaps caused by unread policies. By implementing automated policy tracking in Microsoft 365, compliance managers and HR teams can replace manual follow-ups with automated workflows and real-time completion tracking.