Operations | Monitoring | ITSM | DevOps | Cloud

Dispatching Ansible playbooks with CFEngine

In large organizations and infrastructures, it’s fairly common to use multiple configuration management tools. There are many reasons for this. Different teams may have different preferences, some tools suit certain use cases better than others, and existing systems can come with their own limitations. Whatever the reason, the tools don’t have to work in isolation. In this post, we’ll show how to run Ansible playbooks on CFEngine-managed hosts using Mission Portal.
PHP2Shell: How to Find Vulnerable PHP Versions on Your Devices

Last updated: October 21, 2026. We'll update this article as PHP and Linux distributions publish new information. PHP2Shell is the nickname of two critical vulnerabilities in PHP that let an attacker run code on a web server without logging in. PHP released the fixes on October 21, 2026, and IT and security teams now need to know which of their servers and computers run a vulnerable PHP version, so they can patch those first.

CertKit now has 86 built-in deployment templates

There are lots of ways to get a certificate. Getting it onto your Cisco ISE, IBM i, or WatchGuard VPN is the hard part. We keep making that easier. Since July, CertKit has added 51 new deployment templates, more than doubling the library to 86. Each platform has a built-in deployment template, and most have a deployment guide for the setup details. Setup is just picking a certificate and setting a few variables.

Kosli joins the Plexal & Barclays Eagle Labs Scaleup Programme

Kosli has been selected for the fourth edition of the Scaleup Programme run by Plexal and Barclays Eagle Labs. Following a competitive application process, we’re one of 25 high-growth UK technology companies chosen to take part. The programme is built for companies where growth for scaleups starts to present new challenges, with particular focus on scaling commercial performance, customer expansion, funding, and capital planning.

Certificate Lifecycle Management: How to Track, Monitor And Renew Digital Certificates

Certificate Lifecycle Management (CLM) is the process of tracking every digital certificate an organization uses, from the moment it is requested to the day it is retired. IT, infrastructure and security teams look into Certificate Lifecycle Management when they need to stop certificates from expiring unnoticed, keep up with shorter certificate lifetimes and know who answers for each one.

YouTube Let AI Prototypes Read Production. The Token Did the Work.

TL;DR: Google Cloud’s post of 22nd July 2026 on why AI apps fail in production describes how a YouTube team gets AI prototypes in front of user research in weeks instead of quarters: a prototyping stack that hands each prototype read-only access to live production data through a proxy, keeps its code out of the production binary, and throws the prototype away once the idea is proven.

Antivirus scanning with CFEngine and ClamAV

Is the antivirus on your servers working correctly right now? Installing ClamAV takes a single command. The hard part is keeping it running on all servers, since freshclam fails without indicating a problem, cron jobs disappear, and no one notices until an audit. The new ClamAV module deals with this by ensuring that ClamAV remains operational on all hosts and also indicates to you in the Mission Portal when it isn’t.

Unable to get local issuer certificate, explained

Your site loads in Chrome fine. Then a deploy script, a webhook, or integration calls the same URL and gets this: Python says certificate verify failed: unable to get local issuer certificate. Node says unable to get local issuer certificate, or unable to verify the first certificate. It’s all the same problem. It’s a misconfiguration between your certificate and a trusted root. Either the server isn’t sending it, or the client doesn’t have it.
Sponsored Post

Windows Hardening & Continuous Compliance: Keeping 200+ Security Settings Secure 24/7

Every Operating System – not even counting the software installed on top of it – has a myriad of configuration settings that affect security. Windows Server alone has 4000+ configurable options, out of which 200+ are important for security & compliance efforts. They include: These settings are at the very core of all of your security & compliance efforts – and they are surprisingly often ignored.

AI Agents Hacked 395 Organizations. How Do You Stop Them?

AI agents just changed the speed of cyberattacks. Are security teams ready? In a massive AI-orchestrated cyberattack, hundreds of autonomous AI agents exploited vulnerabilities in PaperCut software, compromising 440 servers across 395 organizations in 48 countries. But the bigger question isn't how these attacks happened. It's how human security teams are supposed to respond when attacks move faster than they can react.

When AI Attacks at Machine Speed, Configuration Management Becomes Cybersecurity

The Australian Medicare AI agent incident highlights a broader shift in cybersecurity. AI does not need to create new vulnerabilities to increase risk. Its ability to continuously discover, test, and pursue existing weaknesses places greater emphasis on maintaining secure configurations over time, not just fixing issues once. Security teams are used to the idea that determined attackers will keep looking for a way in.

CVE-2026-74580: Possible VM Escape via the Vghost Vulnerability

CVE-2026-74580 is a high-severity Linux kernel bug in vhost, the subsystem that accelerates I/O for virtual machines. It gives a local user a reliable path to root on the host, and in some VM setups it lets a guest write into host memory. The CVE record has existed since August 21, 2026, but the full technical write-up, nicknamed "Vghost", only went public on October 12. It came with working exploit demos for both a local root escalation and a VM escape.

Deployment alerts: know when a renewed certificate doesn't land

Renewing a certificate is the easy part. Getting it onto the server is where automation breaks. Somebody rotates the API token on the firewall. A service account password expires. A VM gets rebuilt and the agent never comes back. The certificate renews right on schedule, the deployment fails, and the server keeps serving the old certificate until it expires. Renewed and deployed are not the same thing.

Fixes available for CVE-2026-92392 and other curl vulnerabilities

On 7 October 2026, Daniel Stenberg published a blog post describing a plan to release a new version of curl on 14 October 2026 in order to address 22 known security vulnerabilities. These vulnerabilities have varying severities, with a single vulnerability assessed as high (CVE-2026-92392), while the others have a low or medium severity. The curl maintainer has coordinated with downstream vendors, including Ubuntu, under embargo and the vulnerabilities have been publicly disclosed on the planned date.

SAP Security Patch and Vulnerability Monitoring Guide

Avantra monitors SAP security patch status across entire landscapes, checking each newly published SAP HotNews note against every managed system and tracking which systems still need it. It covers the patch side of SAP vulnerability management, which is a different job from code-level vulnerability scanning.

RISE with SAP Shared Responsibility: Security Monitoring Guide

Avantra handles RISE with SAP security monitoring for the layer that stays with the customer under the RISE with SAP shared responsibility model. SAP operates the infrastructure, network, database, and operating system, while the customer still owns application configuration, users and authorizations, custom code, and requesting the SAP Security Notes that SAP doesn’t apply proactively.

What Is an Antidetect Browser and How Do Teams Use It in 2026?

Modern websites recognize visitors through far more than cookies. Screen resolution, installed fonts, time zone, GPU details, and dozens of other signals combine into a browser fingerprint that can identify a device with surprising accuracy. For operations, marketing, and QA teams who manage many accounts or test from many environments, that creates real friction.

TryHackMe Alternatives for Blue-Team Training

For IT operations teams moving into defensive security, TryHackMe is a common first stop. Its guided rooms run in the browser, and its SOC Simulator has analysts triage alerts and write case reports in scenarios that can run in Splunk, Elastic or Sentinel. As skills develop, training needs change. You might want longer investigations, a certification that fits a development plan, progress reporting across several analysts or labs that look like your own tooling.

The NSA said wildcard certificates are bad. Everyone uses them anyway.

In October 2021 the NSA published an advisory titled “Avoid Dangers of Wildcard TLS Certificates.” It reiterated what security consultants had been saying for years: don’t use wildcard certificates. Single-name certificates per host are safer. Five years later, we counted the certificates that are actually used. One in three domains has a wildcard on it. For.bank domains, where you need a security review just to register, it’s four in five. Operators aren’t careless.

How to Integrate NinjaOne with a SIEM

In this episode of NinjaOne01, Jeff Hunter, Field CTO at NinjaOne, walks through NinjaOne’s new SIEM Exporter App. The app is a dedicated place to set up and monitor the webhooks that send NinjaOne activity data to your third-party SIEM (Security Information & Event Management) system. Note: this is an early access feature, so contact your account manager to have it enabled for your account. What this video covers.

How Configuration Monitoring Helps Detect Zero-Day Activity

Last updated: October 9, 2026 A zero-day vulnerability may be unknown, but its effects often are not. Exploitation can leave behind observable changes: a new privileged account, an altered management setting, an unexpected file, a modified access rule, or configuration drift from an approved baseline. That makes zero-day configuration monitoring an important part of a defense-in-depth strategy.

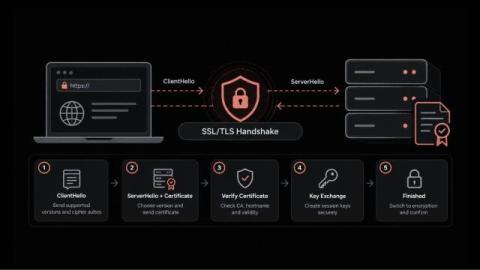
SSL Handshake Guide Covering Each Step and the Fixes That Prevent Outages

Why would a website that passes every uptime check still show customers a security warning? In most cases, the server is running and the network is healthy. The failure happens earlier, during the brief exchange in which the browser and the server agree on how to communicate securely. That moment is the SSL handshake. If it goes wrong, users get an error page while your dashboards stay green. Maybe a certificate expired; maybe a routine change left both sides on different protocol versions.

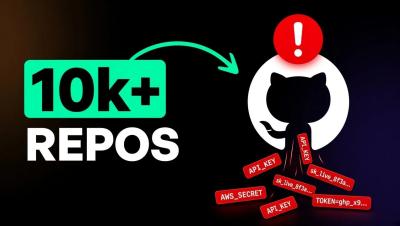
7 Layers of Agent Security (1 in 6 repos has leaked credentials)

I scanned 10,705 public GitHub repos for leaked credentials. After removing obvious placeholders, 3,543 still had something that looked like a key, and 1,680 held almost 7,000 credentials in recognizable formats like Stripe keys. If you're new to coding with agents (or you've been a dev for decades), this is the setup I'd want you to have before you ship anything public.

How Modern Firewalls Help Businesses Strengthen Network Security

As business networks become more complex, the methods used to attack them are evolving as well. Organisations now need to protect cloud services, remote workers, connected devices, internal applications, and large volumes of data, often across multiple locations. Traditional perimeter security alone is no longer sufficient to address this environment.

Certificate monitoring with TLS, chain, and post-quantum readiness

Most customers start CertKit with SSL host monitoring. On day one, you point CertKit at the systems you already run and get every certificate and when it expires. You start with confidence that you have everything under control. Then, you automate, letting CertKit take over the certificates as they need to be renewed. Each renewal is the last time you ever have to worry about that certificate.

Deutsche Bank leads the way on secure adoption of AI enabled software delivery

As AI accelerates software development and expands its scale, Deutsche Bank is taking a leading role in ensuring the technology can be adopted safely, securely, and responsibly across regulated industries. As an investor, Deutsche Bank’s Corporate Venture Capital arm participated in Kosli’s Series A funding round, reinforcing the bank’s view that automated governance will be a key enabler of AI-assisted software delivery in regulated industries.

What's taking DNS-PERSIST-01 so long?

In February, Let’s Encrypt announced that DNS-PERSIST-01 was coming, “some time in Q2 2026.” It’s October, and it’s nowhere close to ready. We’ve been waiting for DNS-PERSIST-01 since January, along with every other ACME client and lots of organizations. DNS-PERSIST-01 promised to simplify domain validation and make automation easier, but we had to wait on Let’s Encrypt. Let’s Encrypt is waiting on a redesign, a standards body, and maybe one more vote.

9 Best AI Penetration Testing Companies for Enterprise Security Teams

Enterprise security teams know the value of penetration testing. The problem is the schedule. A large organization may run hundreds of web applications, thousands of API endpoints, mobile apps, AI features, and a sprawling external attack surface, and much of it changes every week. An annual or quarterly pentest examines a snapshot of that environment, produces a report weeks later, and leaves most of the year untested.

HIPAA Wasn't Written for AI Agents. It Applies to Them Anyway

In short, healthcare is adopting AI agents faster than almost any other industry. More than 85% of Epic’s customers already use Epic AI, Epic’s Agent Factory will let every health system build agents of its own from 2027, and 43% of health systems were piloting agentic AI at the start of this year.

A Simple First-Project Workflow for Trying Seedance 2.5

A first AI video project becomes difficult to evaluate when the idea includes several subjects, changing locations, camera moves, and a detailed story. If the output fails, a beginner may have no clear way to tell what went wrong. A small project gives each revision a useful purpose. Try Seedance 2.5 with one visible action and a simple ending. Treat the first output as a draft to inspect before editing.

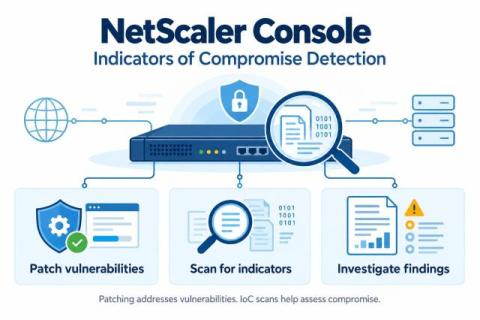
NetScaler Console Indicators of Compromise Detection

On September 27, 2026, Citrix published a security bulletin covering eight new vulnerabilities in NetScaler ADC and NetScaler Gateway. Some of these vulnerabilities are critical and have already been exploited in the wild. Citrix released fixed NetScaler builds and recommends upgrading affected appliances as soon as possible. However, when a vulnerability is already being actively exploited, installing the update only solves part of the problem.