

Operations | Monitoring | ITSM | DevOps | Cloud

What Are the Differences Between On-premises and Cloud-based Log Management?

Cloud computing has changed the way we think about software, and opened up many new possibilities in both business and software development. Log management tools have also been affected by this, which begs the question – what are the pros and cons of cloud log management when compared to on-premises solutions? There are several key things you should consider before opting for either one, so here is a brief overview of the most important aspects that will help you make an informed decision.
Enhancing AWS security with Graylog centralized logging

AWS is a popular destination for IaaS that offers quickly saleable resources to meet even the largest customer demands. Cloud scalability like this can generate a large amount of logs you need to monitor to keep up with your cybersecurity goals. Getting those logs into a SIEM or centralized log management platform such as Graylog is key to have proactive monitoring and alerting.

How to Use Graylog Lookup Tables

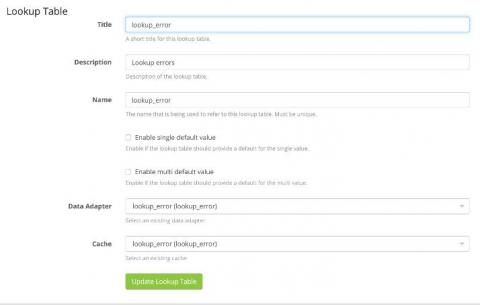
Logs are a wealth of information containing meta-data from IP addresses, User Names, and error codes. While this is all extremely helpful, the task of understanding all this can seem overwhelming at times to an untrained eye. Other times, corporations might have additional resources they would like to enrich their logs with, i.e., adding a department name to a log message that depends on the username in the log.

Strengthening cybersecurity with log forensic analysis

Any system connected to the Internet is vulnerable to malicious attacks and breaches. If it’s online, there’s someone out there trying to break into it and do something bad with it (usually stealing data). Plain and simple. To protect your most valuable assets, you need bulletproof security measures, a skilled SecOps team, robust investigation tools, and reliable prevention/mitigation strategies.

Ingesting Cloudtrail Logs with the Graylog AWS Plugin

Cloudtrail logs provide excellent insight into how your AWS account is being used. They record all activity by the web console, SDKs, and APIs. With help from the AWS plugin, getting this information into Graylog is easier than ever. In this blog post you'll set up the required AWS resources, configure the Graylog input, and do some basic searches to explore its capabilities.

Improving IoT security with log management

The Internet of Things (IoT) revolution has set the beginning of a new age of data transfer. Each day, a massive number of new devices get added to all kinds of network infrastructures, transferring gargantuan amounts of data back and forth. In the next decade, we expect the number of IoTs to grow to a staggering 80 billion connected devices – practically outnumbering the human population tenfold.

Preventing and mitigating data loss with Graylog

If you’re handling sensitive information, dealing with data loss can be more than just a headache. Log management tools such as Graylog can enhance your incident response and management strategies, and help you mitigate the damage when a breach occurs in your database. Minimizing data loss with a fast and scalable logging solution is key if you want to bring your cybersecurity to the next level.

Shipping Office 365 audit logs to Graylog with O365beat

O365beat is an exceptionally useful open-source log shipping tool created by counteractive. With a few simple tweaks, it can be used to fetch Office 365 audit logs from the Office 365 Management Activity API and forward them to Graylog. The best part of this tool is that it leverages all the flexibility and power of the beats platforms such as libbeat.