Operations | Monitoring | ITSM | DevOps | Cloud

Best Anomaly Detection Software: 9 Tools Compared on Cost and Coverage

Does the anomaly you need to catch show up in infrastructure, in security logs, in a data pipeline, or in a revenue figure? If you already know the answer, you probably learned it from an incident. A service degraded quietly, nobody got paged, and the post-mortem showed the signal had been in the data for hours. The thresholds were set correctly, and they still could not separate a busy Tuesday from a failure.

How AI Agents Are Changing ITSM Faster Than We Think | Motadata Webinar

AI is transforming ITSM beyond co-pilots with autonomous AI agents that can understand, decide, and act. In this webinar, discover how AI agents are reducing manual workloads, accelerating incident resolution, improving service quality, and enabling intelligent service operations. Learn real-world use cases, key implementation strategies, and how organizations can move from reactive support to proactive, AI-driven IT service management. Watch now to explore the future of smarter, faster, and more efficient ITSM.

What Is a CBOM and Why Does It Matter?

Quantum computing is reshaping the future of cybersecurity. In this video, learn what a Cryptographic Bill of Materials (CBOM) is, why it matters for post-quantum security, and how it helps organizations identify vulnerable cryptography, prioritize migration, and improve cryptographic visibility. Perfect for security professionals, DevSecOps teams, IT leaders, and compliance teams preparing for the quantum era.

10 Best IT Operations Management Tools (ITOM) Compared for 2026

No IT team sets out to run ten monitoring tools. It happens one purchase at a time. You add a network monitor after one outage, a server monitoring tool after the next, then a log analyzer, then an APM product when the app team gets tired of guessing. Then something breaks, and every one of those tools has an opinion. Each fires its own alerts. None of them agrees on the cause, and the first hour of the incident goes to deciding which screen to believe.

9 Best Log File Analysis Tools for IT and DevOps Teams

An incident is open and the evidence is scattered. The application logs point to a connection timeout; the load balancer shows nothing unusual, and the container that produced the original error was replaced eighteen minutes ago. Three engineers are logged into three separate hosts running the same search, and the log line that would explain it has already rotated away. That is the moment most teams start shopping for a log file analysis platform.

How to Choose the Right Infrastructure Monitoring Tool

A production service degrades, and one question decides the next hour: is it the server, the network, or a cloud dependency? Each layer usually reports into a separate console, so pinning down the answer can absorb an hour the business would rather not lose. The right infrastructure monitoring tool is what turns that hour into minutes. On paper, most monitoring platforms look identical. Each one promises full-stack visibility and shows a polished dashboard.

Post-Quantum Cryptography and How to Prepare Your Organization

Do you actually know where encryption lives inside your infrastructure? Not the vendor's answer. The full map: every TLS handshake, every signed software update, every VPN tunnel, every certificate your systems trust. That map is where post-quantum cryptography starts to matter. The technology has moved from a research topic into a compliance deadline, and the algorithms protecting your data today were built for a world without quantum computers.

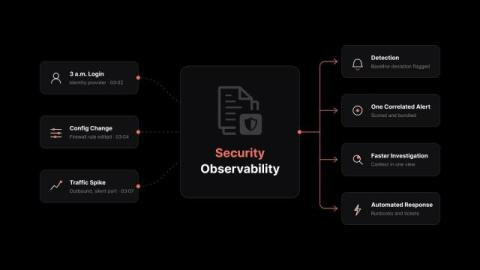
Security Observability: Pillars, Use Cases, and How It Works

When an alert lands, does your team already see the full story, or does the work start with pulling scattered data together from one tool after another? For many organizations it's the second one, where the incident itself takes a backseat while analysts hunt across dashboards. The evidence is right there, scattered across platforms that don't share context. Security observability exists to close that gap.

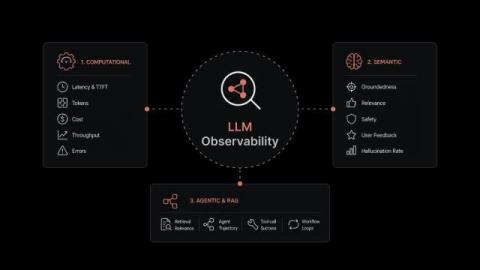
What Is LLM Observability? A Complete Guide

If you run LLM features in production, your most dangerous failures are the ones your monitoring never flags. Your LLM feature passed every test, and the demo went great. Three weeks after launch, a support ticket lands: the chatbot quoted a refund policy that does not exist. The dashboards are all green, and the same prompt answers correctly when you retry it. This is the blind spot LLM observability exists to close. Your existing tools saw the request come back fast with a clean status code.

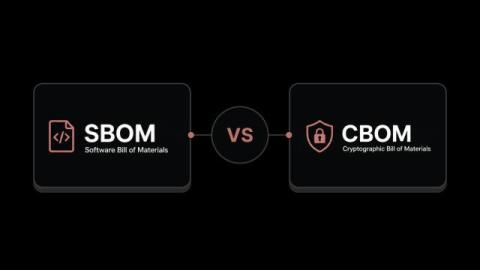
SBOM vs CBOM: Software and Cryptographic Bills of Materials Explained

How confident are you that you know every component inside your software, and every algorithm guarding it? In practice, the answer is usually scattered across build tools, ticketing systems, and spreadsheets that stopped being accurate months ago. A modern application draws on hundreds of open-source parts, and the encryption underneath them is harder still to trace. That visibility gap is what keeps the "SBOM vs CBOM" question alive in security and compliance reviews.