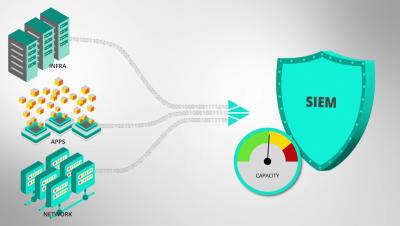
In today’s digital-first world, most security problems are actually data problems, and data volumes are outpacing organizations’ abilities to handle, process, and get value from it. You’ll have 250% more data in five years than you have today, but the chances of your budget increasing to match that are slim. The challenges that come with managing the rise in enterprise data volume directly affect your ability to adequately address cybersecurity risks.
The shortcoming of traditional SIEM implementations can be traced back to big data analytics challenges. Fast analysis requires centralizing huge amounts of security event data in one place. As a result, many strained SIEM deployments can feel heavy, require hours of configuration, and return slow queries. Logz.io Cloud SIEM was designed as a scalable, low-maintenance, and reliable alternative. As a result, getting started isn’t particularly hard.
If you’re in need of new SIEM tooling, it can be more complicated than ever to separate what’s real and what’s spin. Yes, Logz.io is a SIEM vendor. But we have people in our organization with years of cybersecurity experience, and they wanted to share thoughts on how best to address the current market. Our own Matt Hines and Eric Thomas recently hosted a webinar running through what to look out for titled: Keep it SIEM-ple: Debunking Vendor Nonsense. Watch the replay below.
The System Administrator! AKA the Sysadmin. The keeper of the network, computers – well basically all things technology. The one who is hated for imposing complex passwords and other restrictions, but taken for granted when everything works well. They are the first to be called when “facebuuk.com” reports: “domain does not exist”.
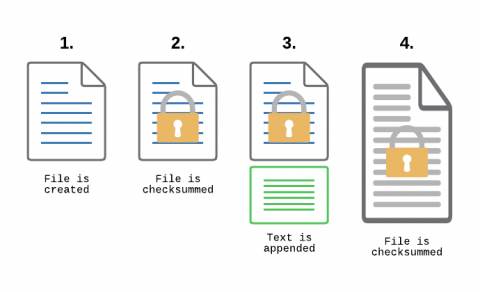
File Integrity Monitoring, aka as FIM, is a must-have feature for anyone in charge of security. With FIM, one can detect when a critical file, such as a file that belongs to the Operating System, or a key configuration file, is changed. In most cases, configuring FIM is straightforward: If the file changes then generate an alert.
A SIEM (Security Information Event Management) platform, along with several other tools that make you crave Alphabet Soup (XDR, UBA, NDR, etc), is a critical component of any organization’s security infrastructure. Between a constantly growing volume of logs, increasing attacks and breaches, and challenges finding qualified staff, many organizations may consider a SIEM migration. There could be several reasons for this.
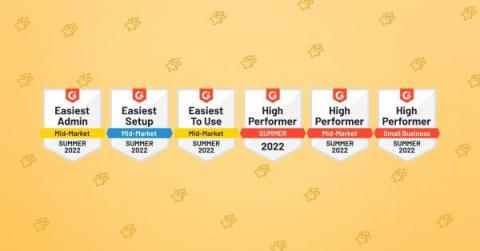
For Summer 2022, Logz.io is thrilled to have earned six G2 Research Badges for our Cloud SIEM offering. These honors highlighted the ease of setup, ease of use, and high performance that we provide our customers through Cloud SIEM. G2 Research is a tech marketplace where people can discover, review, and manage the software they need to reach their potential.