Operations | Monitoring | ITSM | DevOps | Cloud

The latest News and Information on Log Management, Log Analytics and related technologies.

Logz.io Named a Leader in GigaOm Radar for Cloud Observability

Today we are excited to share a key milestone, not only for Logz.io, but also for our industry as a whole. For the first time ever, an industry analyst took on the ambitious challenge of analyzing and assessing several different markets including monitoring and telemetry, APM, AIOps, observability, and more. The radar also takes account of evaluating leaders’ various products, unveiling a comprehensive overview under the unified lens of Observability.
Up Close Monitoring with SignalFlow

It’s April, and that means it’s Mathematics and Statistic Awareness month. And in our everyday world of monitoring and observability, both play an ever-increasing role in how we keep track of our environments, both our apps and our infrastructure. Our world is no longer about just pinging the server/app to make sure “It’s alive!”.

Using Telegraf to Collect Infrastructure Performance Metrics

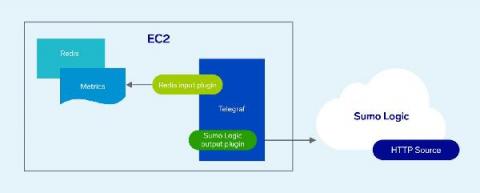
Telegraf is a server-based agent for collecting all kinds of metrics for further processing. It’s a piece of software that you can install anywhere in your infrastructure and it will read metrics from specified sources – typically application logs, events, or data outputs.

Troubleshooting Firewall Issues in DigitalOcean

DigitalOcean is a cost-effective virtual private server (VPS) provider popular among the developer community. The platform also offers services for rapid development, deployment, testing, and maintaining modern distributed applications. One of these services is a managed firewall solution that allows blocking unwanted traffic. It’s relatively easy to manage and deploy as an infrastructure component. Sometimes, however, operations teams need to dig deeper when the firewall blocks network traffic.

How Does Archiving Work in Graylog?

Every week we get many great questions through support, the community, social media, and our weekly demo. On Fridays, I like to share the most common questions and answers, tips, insights, a closer look at Graylog, interviews, etc. If you have any questions for me, drop them on Twitter, and I’ll do my best to fold them into upcoming Friday posts. Our handle is @graylog2.

Building Kibana dashboards more efficiently

Creating dashboards is quicker and easier than before with a new streamlined navigation experience, now available in Kibana 7.12. This dashboard-first approach makes it simple for you to create and add visualizations without leaving your dashboard-building flow. Get started directly from a Kibana dashboard with a few simple steps: Select Create Panel and choose what type of visual you want to build.

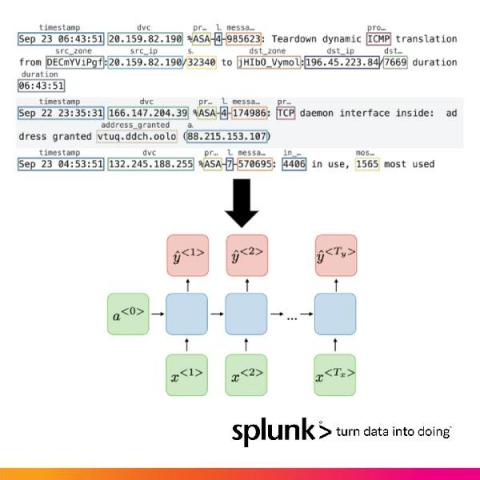
How Splunk Is Parsing Machine Logs With Machine Learning On NVIDIA's Triton and Morpheus

Large amounts of data no longer reside within siloed applications. A global workforce, combined with the growing need for data, is driving an increasingly distributed and complex attack surface that needs to be protected. Sophisticated cyberattacks can easily hide inside this data-centric world, making traditional perimeter-only security models obsolete.

Logit.io's Response To The Elasticsearch B.V. SSPL Licensing Change

On the 14th of January 2021, Elasticsearch B.V. announced that future releases of Elasticsearch and Kibana would be released under a dual license SSPL (Server Side Public License). As a result of this change it is evident that the components that make up Elasticsearch and Kibana in version 7.11 (and onwards) of the ELK Stack will no longer be considered as open source based upon the Open Source Initiative's requirements for licensing.