Operations | Monitoring | ITSM | DevOps | Cloud

The latest News and Information on CyberSecurity for Applications, Services and Infrastructure, and related technologies.

Kubernetes Master Class Security & Observability feat. Tigera

In this RKE-focused workshop for networking, security, and observability on containers, Kubernetes, and Calico, you will work with a Calico and RKE expert to learn how to design, deploy, and observe security and networking policies in an RKE environment. This 90-minute hands-on lab comes with your own provisioned Calico Cloud environment, designed to provide more complete knowledge on how to implement:– Workload access controls– Compliance and reporting– Run-time visualization of traffic flow and security policies– Service-level observability– Anomaly detection and live troubleshooting You will come away from this workshop with an understanding of how others in your industry are doing Kubernetes, container and cloud security, and observability in RKE, and how you can implement it in your own organization.
Kubernetes Master Class Managing Cluster Security at Scale

A Kubernetes cluster has various attack surfaces, from the API server to application traffic. It's important to understand what these potential areas of attack are, and from there, work out the best ways to mitigate the risks. This is especially important when managing multiple clusters. You want to ensure that you are following the right methods, and then standardizing those security approaches to be applied to all your clusters. In this session, we will cover some of the Kubernetes attack vectors and detail how to secure your clusters.

Top title alert! Ivanti recognized by Frost & Sullivan's 2021 Best Practices Award as Asia-Pacific Secure Remote Access Company of the Year

We’re thrilled to announce that Frost & Sullivan has awarded the 2021 Asia-Pacific Company of the Year Award for secure remote access to Pulse Secure (acquired by Ivanti). In determining awards, Frost & Sullivan “applies a rigorous analytical process” that includes “detailed evaluation of best practices criteria.”

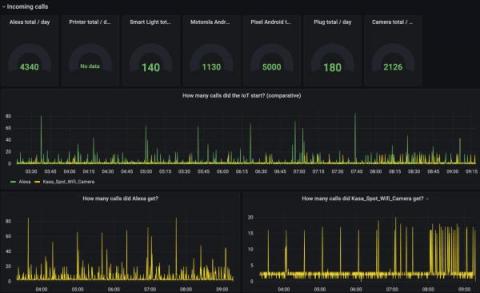
Visualizing IoT security metrics with Grafana at Network to Code

As the number of connected gadgets in our homes, offices, and industrial networks continues to grow exponentially, keeping IoT devices secure has become a vital part of our everyday lives. However, our webcams, printers, and smart plugs often lack security features due to their fast time to market, making them particularly vulnerable to attack. And because security metrics themselves can be tricky to assess, tracking IoT device security is increasingly a challenge.

Turbocharging AKS networking with Calico eBPF

A single Kubernetes cluster expends a small percentage of its total available assigned resources on delivering in-cluster networking. We don’t have to be satisfied with this, though—achieving the lowest possible overhead can provide significant cost savings and performance improvements if you are running network-intensive workloads.

U.S. Government Issues Advisory Against Common Cyber Threats During the Holidays

In advance of this week’s Thanksgiving holiday in the U.S., the U.S. Cybersecurity & Infrastructure Agency (CISA) and the Federal Bureau of Investigation (FBI) issued a reminder for critical infrastructure to stay vigilant against cyber threats during holidays and weekends. This advisory is a reminder the holidays present a noted challenge for businesses and an opportunity for cyber adversaries.

Kubernetes Security: 9 Best Practices for Keeping It Safe

Kubernetes dominates the container orchestration market in every way. According to the latest State of Kubernetes and Container Security study, 88% of enterprises utilise Kubernetes to manage a portion of their container workloads. Kubernetes and other orchestration systems have given software deployment and management a new level of robustness and customization. They also brought attention to the current security landscape's shortcomings.

Better Protect your Corporate Data While Ensuring Optimal Service Delivery for your Business Lines

Within an organization, the Network Operations Center (NOC) and Security Operations Center (SOC) teams need to work together to maintain optimal network performance in addition to ensuring both overall security and the availability of IT services for business lines. In the past, these two teams were focused on two separate objectives, using different tools to do so and often running specific processes.

Mail Assure achieves top result in Virus Bulletin testing

We’re pleased to announce that N-able™ Mail Assure has received a top result in an independent test conducted by the Virus Bulletin, an industry-renowned test laboratory and an important reference for specialists and businesses concerned with computer security. So, what exactly is this test and how did Mail Assure achieve such a great score?

You've Achieved GDPR Compliance-Now What?

General Data Protection Regulation (GDPR). Most of us remember the months and weeks leading up to the deadline. We did whatever needed to be done to achieve compliance. Now it seems like a distant memory. And the pressure is mostly off. But in other ways, it was just the beginning. As you continue creating your day-to-day compliance strategy, you might find that the tactics that got you to the finish line were more short-term solutions that won’t necessarily stand long-term.