Operations | Monitoring | ITSM | DevOps | Cloud

The latest News and Information on Log Management, Log Analytics and related technologies.

Ronald van Loon & Sendur Sellakumar | Splunk Cloud Is Rebuilt for the Data Age

Data analyst Ronald van Loon sits down with Splunk’s Sendur Sellakumar to discuss how companies can succeed in the data age. The conversation covers shifting to a cloud-native experience, honing in on a data-to-everything strategy, and customer-centric approach to data and product development. The majority of organizations are not prepared for an influx of data on the scale promised by the dawning data age. To thrive, every organization needs a complete view of its data — real-time insights with the ability to take real-time action.
Monitor Applications Running in DigitalOcean Droplets

We’re happy to announce SolarWinds is partnering with DigitalOcean, a cloud infrastructure provider offering cloud services to help deploy modern apps, to offer application level monitoring to applications running in droplets with SolarWinds® application performance management (APM) solutions.

Getting started with Elastic Cloud on AWS

Elastic on Amazon Web Services (AWS) gives you the power of Elastic Enterprise Search, Elastic Observability, Elastic Security as well as the Elastic Stack. You can quickly and easily search your environment for information, analyze data to observe insights, and protect your technology investment. Elastic Cloud lets you deploy your way, whether as a managed service or with orchestration tools you manage in the cloud.

Onboard your tracing data to Sumo Logic even faster with AWS OpenTelemetry distro (preview)

We at Sumo Logic believe in an open, flexible, community-driven approach to collecting observability data. Those reasons are outlined in one of my recent blogs. In that publication, I share the belief that an application’s observability gains traction from the fact that telemetry signals are designed, composed, and produced by an application developer/vendor in compliance with industry standards, and are not a proprietary, black box component of the monitoring vendor.

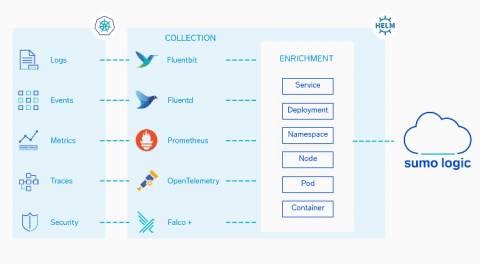
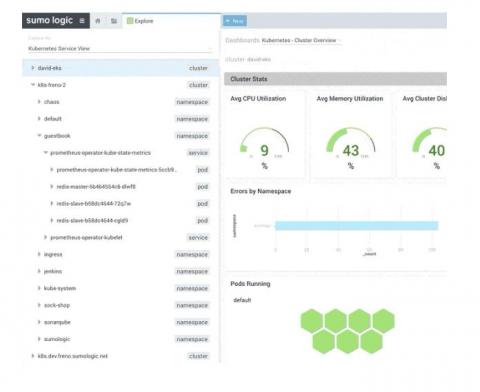
Sumo Logic partners with AWS to monitor Amazon EKS Distro

Today Amazon announced Amazon EKS Distro, a distribution for Kubernetes based on and used by Amazon EKS. Amazon EKS Distro enables you to create secure and reliable Kubernetes clusters using the same versions of Kubernetes and its dependencies deployed by Amazon EKS. Each Amazon EKS Distro release follows the EKS process, verifying new Kubernetes versions for compatibility.

Monitor Amazon EKS Distro (EKS-D) with Splunk Infrastructure Monitoring

We are excited to partner with AWS in launching Amazon EKS Distro (EKS-D), the official Amazon Kubernetes distribution, which includes the same secure, validated, and tested components that power Amazon EKS. Splunk Infrastructure Monitoring provides a turn-key, enterprise-grade Kubernetes monitoring solution for Amazon EKS. Additionally, Splunk Infrastructure Monitoring provides out-of-the-box monitoring of Kubernetes Control Plane.

5 Essential MySQL Database Logs To Keep an Eye on

MySQL is the de facto choice for open-source relational databases, and you should learn how to use MySQL database logs to improve efficiency and security. As an open-source product, it is free to use and has a large and active developer community. It is crucial to understand how to diagnose and monitor the performance of a MySQL instance in the long run. Logs to the rescue!

How to Maximize Logging Performance with Kafka

As software is evolving away from monoliths and towards service-based architectures, it is becoming more apparent than ever that logging performance needs to be a first-class consideration of our architectural designs. This article will explore how to build and maintain a logging solution for a microservice-oriented containerized application, how to address some common difficulties which come with running such a solution, plus some tips for debugging and eliminating bottlenecks.

What You Need to Know About IoT Logging

The Internet of Things (or, IoT) is an umbrella term for multiple connected devices sharing real-time data, and IoT logging is an important part of this. Troubleshooting bug fixes, connection problems, and general malfunctions rely heavily on logs, making them an invaluable asset not only in designing systems but also in system maintenance. To maximize system potential, this plethora of generated data needs to be managed efficiently.

Announcing auto-complete with type hints in the Elasticsearch Python client

Python introduced support for type hints in Python 3.5 via PEP 484, allowing tools like Mypy and Pyright to check your Python code for type conflicts before execution. This also helps tools that provide code auto-complete — like IDE, IPython, and Jupyter Notebooks — by providing a complete function signature, even for functions that are generated on import time like the Elasticsearch Python client.