Operations | Monitoring | ITSM | DevOps | Cloud

The latest News and Information on Cloud monitoring, security and related technologies.

Mike Rahmati: My Serverless journey with Cloud Conformity

Mike Rahmati is the Head of the Advisory Board at Dashbird. He is the Co-Founder and CTO of Cloud Conformity (acquired by Trend Micro) – a Cloud Security Posture Management Solution – one of the largest and earliest adopters of serverless. Mike is also an active AWS Community Hero. In this article, he shares his journey and experience with serverless. Cloud Conformity was founded in 2014 as a result of our own experience of issues migrating to the cloud.
AWS Well-Architected Workload Recommendations in Splunk

The Well-Architected Tool is a new AWS service that compares the state of your workloads with AWS architectural best practices. Splunking your workload state and improvement recommendations will give you better insights into your applications as well as best practices to follow along your cloud journey. The Well-Architected integration in Grand Central will give you workload insights broken down by the following 5 pillars.

How to Remediate Unencrypted S3 buckets

Cloud environments are always susceptible to security issues. A significant contributor to this problem is misconfigured resources. Traditional IT Infrastructure was somewhat static; server hardware only changed every few years. With few changes occurring, security was also more static. The modern cloud environment is a much different challenge. In cloud environments, servers, services, and storage are created with automation, resulting in a dynamic and potentially ever-changing server environment.

Datadog on Serverless

The Datadog Security Platform team leverages Serverless to ingest security events across many different cloud providers, deployment platforms, and devices. These security events are then transformed and shipped to a data lake to help defend and protect the platform as a whole. Once there, these ingested events are used to drive internal investigations, create internal security alerts, and reason about security incidents.

AWS and Grafana Labs are working together on cloud native observability

Cloud native observability is at a watershed moment. The explosion of microservices has created previously unseen amounts of monitoring data, limiting the ability of humans and computer systems to extract meaning from data with last-generation tools. Debugging is often a process of detecting correlation, and then turning correlations into causal connections. This is where modern cloud native tooling comes in.

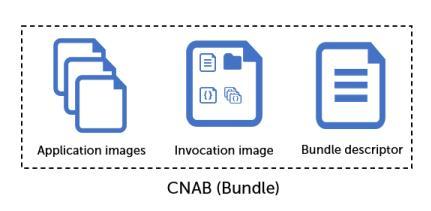
Installing Mattermost using the Azure CNAB Quickstart Library

TL;DR – Get started with Mattermost on Azure using the Mattermost on AKS quickstart from the Azure CNAB Quickstart Library. The quickstart provides a fast and simple way to get running with Mattermost, without the need to learn or install any new tooling. By using Azure Kubernetes Service (AKS), the infrastructure is fully managed for you, and the quickstart handles configuring networking and SSL certificates so you can instantly access the Mattermost application after installation.

Announcing Honeycomb support for event ingestion with OTLP

Today, AWS announced enhancements for AWS Distro for OpenTelemetry. We’re working with AWS to build in additional support from partners. In tandem with that launch, Honeycomb is announcing support for event ingestion using OpenTelemetry Protocol (OTLP). With that change, you can simplify management overhead and configuration by no longer needing to maintain a separate OpenTelemetry exporter.

Dashbird Round-Up 2020

It’s safe to say that 2020 has been quite the year for everyone, and at Dashbird we’ve had quite a few changes of our own. It became the year full of improvements, growth, and feature releases that we had only imagined a year ago. This is our round-up of all the feature releases we launched this year. Just starting out with Dashbird? Great, you are in the right place.

Secure Your Cloud Transformation with Continuous Intelligence

CrowdStrike and Sumo Logic work together to identify security threats and defend against IOCs in a hybrid environment. Customers gain knowledge on adversaries which may be targeting their assets and organisation via strategic, operational and technical reporting and alerts. During this session, we’ll hear from Australian private health provider, NIB, on how Sumo Logic and CrowdStrike have worked together to help NIB secure its digital transformation and cloud environment.