The latest News and Information on Monitoring for Websites, Applications, APIs, Infrastructure, and other technologies.
As an open source company that grew out of a side project in 2008 to an application and performance monitoring platform (APM) used by over 3.5 million developers, Sentry is committed to open source and the community of developers maintaining and building in the open. Similarly, we take a public approach to building our software, which is why it’s a natural extension of our values to announce our support for OpenTelemetry (or OTel), the leading open standard for observability.
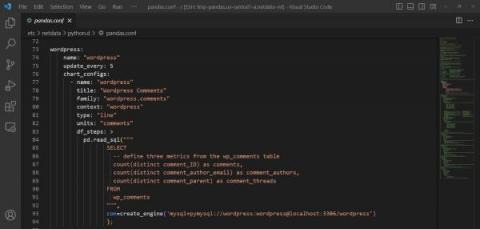
We recently got this great feedback from a dear user in our Discord: This is great and exactly what we want, a clear problem or improvement we could make to help make that users monitoring life a little easier. This is also where the beauty of open source comes in and being able to build on the shoulders of giants - adding such a feature turned out to be pretty easy by just extending our existing Pandas collector to support SQL queries leveraging its read_sql() capabilities.
As part of Nexthink’s launch of the new Nexthink Infinity Platform we also launched Collaboration Experience – adding detailed Microsoft Teams and Zoom call telemetry and insights to the comprehensive “See, Diagnose & Fix” capabilities of the platform. After 4 months, we are ingesting telemetry from almost 2 million employee calls and sessions a day – great testimony to the power and scalability of the Nexthink Infinity platform.
Kubernetes Secrets are a built-in resource type that's used to store sensitive data. This blog teaches you how to work with Secrets in Kubernetes. Kubernetes can do many things, but we usually refer to it as a “container orchestrator.” Orchestrating containers means starting and restarting them when needed, ensuring their configuration matches the declared state, and autoscaling them. But Kubernetes can do much more than that.
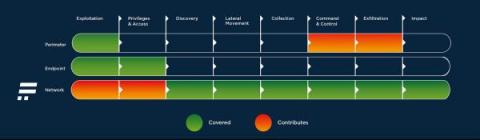
The risk from insider threats has grown massively, with perpetrators frequently getting around organizations' increasingly complex perimeter protections. It is one of the most common ways customer data or industrial and trade secrets leak. This very complex topic includes many types of threats and techniques. Let's discuss how you could detect insider threat activity at a network level.