Operations | Monitoring | ITSM | DevOps | Cloud

The latest News and Information on CyberSecurity for Applications, Services and Infrastructure, and related technologies.

What is Linux Patch Management? Overview & Best Practices

In this article, you will learn more about what is Linux Patch Management, its importance, common challenges, key components, tools, and effective strategies. Managing patches is necessary to maintain a secure, stable and high-performing Linux environment. Whether you’re a systems administrator, IT manager, or responsible for keeping Linux systems running smoothly, mastering the process of identifying, testing, and deploying patches plays an important role in safeguarding your infrastructure.

HIPAA Compliance 101: Securing Patient Data with DevOps

In healthcare, protecting patient data isn’t just a requirement—it’s essential. As a tech lead or DevOps professional, understanding HIPAA compliance is crucial. This guide breaks down the essentials and shows how DevOps practices can streamline the process.

Feature Friday #25: Unprivileged execution

Generally, cf-agent runs as a privileged user. But did you know that you can also run as an unprivileged user? A major benefit of running cf-agent unprivileged is the ability to prototype policies during development. However, attempting to execute cf-agent as an unprivileged user without proper configuration will result in errors.

How to Get Started with a Security Data Lake

Modern SecOps teams use Security Information and Event Management (SIEM) software to aggregate security logs, detect anomalies, hunt for threats, and enable rapid incident response. While SIEMs enable accurate, near real-time detection of threats, today's SIEM solutions were never designed to handle the volume of security data organizations generate daily. As daily log ingestion grows, so do the costs of data management.

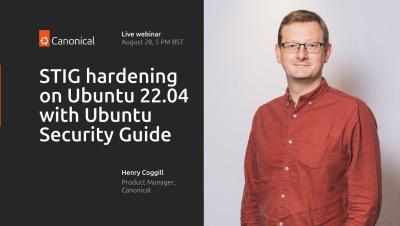
STIG hardening on Ubuntu 22.04 with Ubuntu Security Guide

In this webinar, Henry Coggill will showcase USG (the Ubuntu Security Guide) and demonstrate how it can automate compliance requirements. We will discuss the hardening profiles that are available, including DISA-STIG and CIS benchmarks, then cover setting up and configuring the tool and demonstrate the configuration options that you can make for maximum security and coverage of the STIG rules.

How to install Calico Enterprise on Windows with HostProcess containers

When enterprises transition to a microservices model, they often need to migrate their legacy applications to the new infrastructure. One popular framework used for these traditional applications is.Net. Due to migration, enterprises require the ability to run Windows containers in their Kubernetes infrastructure.

5 Steps to getting started with Zero Trust

In the previous two blogs, we’ve traced the outline of Zero Trust from philosophy and principles to frameworks and marketing terms. In this blog Pete Roythorne talked to Marc Barry, Co-Founder and Chief Product Officer at Enclave, about how you can get started with Zero Trust Network Access. You can read the previous blogs here: To do this we’re going to use CISA’s Zero Trust Maturity Model as a baseline for understanding.