Operations | Monitoring | ITSM | DevOps | Cloud

The latest News and Information on Log Management, Log Analytics and related technologies.

Malicious Claude Code extension in the Cursor marketplace: Coralogix Security Advisory

The Claude Code extension in the Cursor marketplace was compromised for a short period of time today. Watch this security advisory from Chris Cooney and Hetram Yadav, threat detection and response manager at Coralogix, to understand: How the malicious attack operates How to know if you're affected How Coralogix is supporting customers.
FortiGate, PAN-OS and Zscaler dashboards: get firewall logs into the fields they read

FortiGate, PAN-OS and Zscaler now each have a six-dashboard pack in the Dashboard Library, live on every Logs stack. If your firewall logs already arrive as parsed module fields, the Library pre-selects the matching pack. If they don't, it won't, even when the firewall has been sending syslog for years. This post is about that gap: which parsed fields each pack reads, the Filebeat module settings that produce them, and the API checks that tell you whether the dashboards will fill before you install them.

Elastic is a Strong Performer in The Forrester Wave for AIOps Platforms, Q4 2026

Open architecture, explainable AI, and full context Elastic was named a Strong Performer in The Forrester Wave: AIOps Platforms, Q4 2026, which evaluated 10 providers across 24 criteria. Forrester gave Elastic the highest possible scores in five criteria: algorithmic trust and explainability, observability as code (OaC) and GitOps alignment, AI stack and semantic observability, sovereign deployment and data isolation, and pricing flexibility and transparency.

Ship SecOps changes like software: Modernizing the SOC without breaking what works

Cribl gives security teams control over their data: what they collect, where to send it and how much to keep. The rest of the SecOps stack hasn’t kept pace. Detections, parsers and configurations spread across SIEMs, pipelines and data lakes still change by hand, so every cost cut, migration or new source turns into weeks of manual validation, and plenty of planned changes never happen at all. SecOps as Code closes that gap: every change ships like software, with testing, version control and rollback across the entire infrastructure.

Can Observability Reduce Your Tech Debt? | Live Laugh Logs Ep. 5 with Wilco Burggraaf

Your telemetry data can reduce engineering complexity AND make your software more sustainable - find out how in this episode! Welcome to Episode 5 of Live Laugh Logs, the podcast from the Coralogix Developer Relations team. This week, Annie is joined by Wilco Burggraaf, Principal Lead at HighTech Innovators and host of the Sustainable IT Action Netherlands meetup.

What's new in Papertrail: Q3 2026

Q3 was a big quarter for Papertrail. You can now ask questions about your logs in plain English, explore structured logs by field, inspect any single log event in detail, and archive to your own S3 bucket with a setup that keeps you in control of access. We also shipped a round of smaller improvements that make sending logs and searching them faster and smoother. Here is a quick overview. The two Preview features have their own deep-dive articles, linked below.

Dashboard Library: why some dashboards arrive ticked and others don't

Open the Dashboard Library on a Logs stack that already receives Nginx logs and a few cards come up ticked with a green Data detected badge. Others in the same pack sit there unticked. That isn't random. Before it shows you anything, the Library checks what your stack actually holds and pre-selects only the dashboards it expects to fill.

39% of Coralogix sessions are now headless

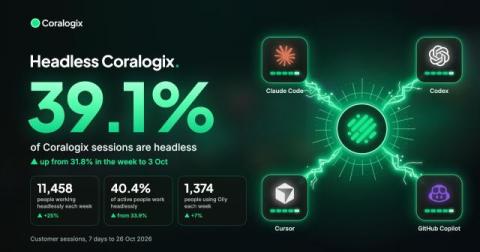
We set out to understand how customers were using Coralogix from outside the web app. Olly answers questions about a system in plain language. Coding agents query logs, examine traces, read metrics and configure the platform through the Coralogix CLI and MCP server. We wanted to see how much of this was becoming part of everyday work. In the week of 20–26 October, 39% of Coralogix sessions included Olly, the CLI or MCP.

Meet the new Explore: every question, one place

From the first alert to the root cause, without leaving the page. TL;DR: Investigating an incident is a series of quick questions, each one leading to the next. Until now, Explore made you stop between questions to translate them into syntax, switch modes or rebuild a chart. The new Explore lets you go straight from one question to the next: one workspace, any dataset, any team, any way you like to ask. Here’s what that looks like on a real night on call.