Operations | Monitoring | ITSM | DevOps | Cloud

Security Businesses Should Never Neglect

Security needs to be a key component of any business operation. These days, there are numerous security threats that organizations of all sizes and in all industries face. Security issues can be the downfall of any business and hard to recover from, so it is vital that business owners prioritize security and know how to protect their business. So, what security should businesses focus on and never neglect? There are a few key areas that you should address that will help you develop strong protection against the most prominent security threats. Keep reading to find out what security you must not neglect.
Announcing Sift: automated system checks for faster incident response times in Grafana Cloud

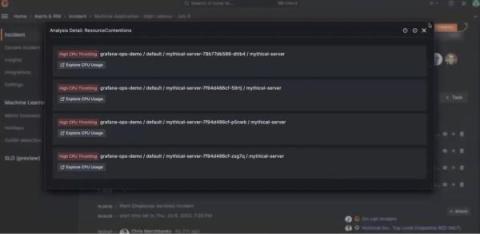
When faced with an incident, there are two areas that demand your immediate attention: the incident investigation, and the cross-functional coordination needed to resolve the issue. Grafana Incident helps with the collaboration by providing a central hub for communication across teams that seamlessly integrates with the tools you are already using, such as Slack or Microsoft Teams. But how can you best use your telemetry data to debug your application and bring your systems back online?

From Alarms to Action: Enhancing Business Security Response Protocols

There's nothing harder than starting and running a successful business in today's modern and competitive society. As a business owner, you have lots to think and worry about, aside from profit margins and customer satisfaction. If you want to keep your business afloat, you also have to think about security and safety and make sure everything is up to par.

Streamlining incident response: the power of integration in engineering tools

In the ever-evolving world of software development, incidents are bound to happen. Whether it's an unexpected server crash, a critical bug impacting user experience, or a security breach, handling incidents swiftly and effectively is crucial for maintaining a seamless user experience and preserving business reputation. That's where incident response tools come in — to help you automate, document, communicate, and mitigate.

Tools and Trends in Site Reliability Engineering according to Gartner's 2023 Hype Cycle

Gartner recently published its Hype Cycle for Site Reliability Engineering, 2023, report. This blog reviews the future of site reliability engineering based on Gartner’s Hype Cycle. Additionally, the OnPage team is pleased that Gartner mentioned OnPage as a sample vendor in the Automated Incident Response category.

Synced for Success: OnPage & Slack for Incident Response

As the post-pandemic world finds its footing again, a resilient spirit drives the revival, propelling businesses to embrace a new era of technological innovation. Notably, IT teams are swiftly adopting the digital transformation of their processes, particularly in incident response. From virtual collaboration tools and remote IT support to automated incident management, teams have found innovative ways to ensure seamless business continuity while delivering IT services with minimum downtimes.

The First 48 Hours of Ransomware Incident Response

The first 48 hours of incidents response is the most critical. We will explain few important steps that need to be taken to mitigate the impact on service availability, information systems integrity and data confidentiality. The cyber resilience is also covered by the individual national regulations and directives, so let's take a closer look at it and explain why principles of Network Detection and Response shall be a crucial part of technical measures implementation for regulated entities.

How to Maximize Time Savings and Reduce Toil During Incident Response

Incidents are a costly burden on businesses. Despite assembling the right people and teams, the manual work, tool setup and prolonged tasks can negatively impact customer experience. The need for adaptable processes to address diverse incident types further complicates the situation. This is where the PagerDuty Operations Cloud steps in. It streamlines and automates all the various manual steps in the incident response process.

The differences between reactive vs proactive incident response

Most commonly, businesses take a reactive approach to incident management. After all, the concept of incident response seems inherently reactive. However, it is possible—and often necessary—to take more proactive measures. This entails identifying potential problems and taking steps to remediate them before they become incidents.

From Monitoring to Action - Get Faster Incident Response with Change Forensics

In this post you’ll learn how Kosli’s Change Forensics gives DevOps, Platform, and Site Reliability Engineers the ability to rapidly pinpoint and understand changes and events in their infrastructure and applications, and get to the cause(s) of an incident quickly.