The latest News and Information on CyberSecurity for Applications, Services and Infrastructure, and related technologies.
As multi-cloud architectures grow in popularity, more and more organizations will start asking how to secure multi-cloud environments. Some will conclude that a multi-cloud architecture requires a fundamentally different approach to cloud security. That’s one example of a myth about cloud security in a multi-cloud architecture. Let’s take a look at why this assumption is flawed, along with some other common myths about multi-cloud security.
User and entity behavior analytics (UEBA) is a relatively new category of cybersecurity tools that utilize machine learning (ML) algorithms to detect abnormalities in the behavior of the users and entities that belong to an enterprise network. UEBA monitors and continuously learns from the behavior of various user accounts and devices in the network, and establishes a baseline behavioral profile for each using statistical and probability models.
Among the different types of cyberattacks, insider threats are the hardest to track and have the highest rate of success. This can be attributed to their use, or rather misuse, of legitimate credentials, machines, and access privileges. Traditional SIEM solutions use simple rule-based alerting to detect potential insider threats, which cannot analyze user behavior or detect any anomalies therein.
Read the latest news on Magecart attacks! We’ve trawled the web for the latest news of data breaches, including updates on previous attacks with insights from our own Security Researcher.
Transport Layer Security (TLS) is a cryptographic protocol commonly used to provide secure network communication between web servers and browsers. TLS has been the main communication security strategy since 2015, when its predecessor, Secure Sockets Layer (SSL), was declared insufficiently secure by RFC 7568.
We are excited to announce the general availability of Tigera Secure 2.5. With this release, security teams can now create and enforce security controls for Kubernetes using their existing firewall manager.
The current business environment requires organizations to implement cybersecurity safeguards to avert disasters associated with breaches, loss of data and hefty fines. Simply implementing a cybersecurity plan isn’t enough, it’s also important to incorporate the right solutions and workflows to prevent a disaster. This post will discuss the current state of cybersecurity, highlighting what organizations should be mindful of to successfully defend against malicious parties.
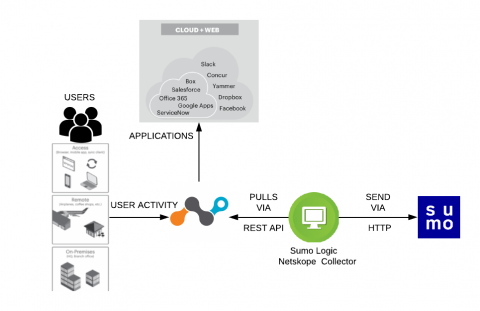
As the worldwide spending on SaaS spending will make up more than half of all public cloud services spending through 2019, it is critical to have end-to-end visibility into threats across your SaaS and on-premise applications. Sumo Logic and Netskope are collaborating on a technical integration that will help joint customers use Sumo Logic to correlate, validate and investigate Netskope alerts into their overall security incident investigation process and understand SaaS application usage patterns.
On [2019-07-29 Mon] we released new builds of our Enterprise Hub packages for 3.12.2 and 3.14.0. This release addresses CVE-2019-10164. PostgreSQL versions 10.x before 10.9 and versions 11.x before 11.4 are vulnerable to a stack-based buffer overflow. Any authenticated user can overflow a stack-based buffer by changing the user’s own password to a purpose-crafted value. This often suffices to execute arbitrary code as the PostgreSQL operating system account.