Operations | Monitoring | ITSM | DevOps | Cloud

Analyze Metric and Event Data on the Same Platform

Analyze both metric and event data on the same platform regardless of source or structure. With Splunk metric indexes, you can quickly and easily ingest, store, and analyze metrics — whether in the Analytics Workspace or with SPL — so you can deliver positive business results. Get the most value out of your data with Splunk.
Virtual Time Series Meetup - April 2020

Virtual Time Series Meetups are events for everyone who is passionate or curious about time series data and how it can be used. In the April edition of our meetup, special guest Saiyam Pathak shares the what, why and how of time series database InfluxDB. The talk features several demos on Kubernetes that can be performed by the viewers. Saiyam also discusses Telegraf, its plugins, and uses Kubernetes plugin during the demo(s).

Elasticsearch Update Index Settings

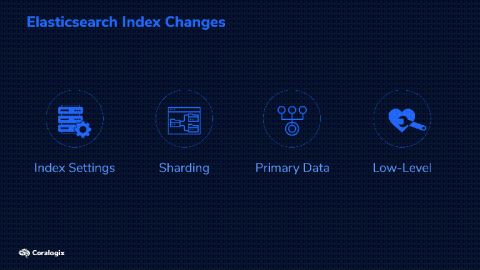
You’ve created the perfect design for your indices and they are happily churning along. However, in the future, you may need to reconsider your initial design and update the Elasticsearch index settings. This might be to improve performance, change sharding settings, adjust for growth and manage ELK costs. Whatever the reason, Elasticsearch is flexible and allows you to change index settings. Let’s learn how to do that!

Sumo Logic Recognized as Data Analytics Solution of the Year Showcasing the Power of Continuous Intelligence

We’re excited to share that our Sumo Logic Continuous Intelligence Platform™ was recently recognized as the Data Analytics Solution of the Year by Data Breakthrough. We join an impressive list of innovative solutions and companies that are solving complex and critical problems and disrupting new markets and industries. Winning this achievement further validates our vision to provide a solution that is helping modern businesses thrive in today’s Intelligence Economy.