Operations | Monitoring | ITSM | DevOps | Cloud

AI SRE Agent MCP Authentication by Header: Keep Keys Out of the Config

Nobody wants an API key sitting in an agent's config file on a shared server. Mike shows how AURA takes the credential off the request instead. AURA can hold your keys in its config file, but it does not have to. Mike Shearer, one of AURA's creators, walks through the alternative: AURA reads named headers off the incoming request and forwards them to the MCP servers it calls, so the credential never has to sit on disk.
AI SRE Agent Approval Workflow: Identity Forwarding to MCP Servers

Two engineers can hold the same approve button and still not be allowed to make the same change. The key riding with the approval settles it. AURA's human in the loop config gates the create_pipeline tool on the Mezmo MCP server and sends each request to a webhook for review. A mock UI stands in for the approval system here, and Mike walks through the payload schema so you can point it at your own.

AI SRE Agent ChatOps: How AURA Runs in a Slack Incident Channel

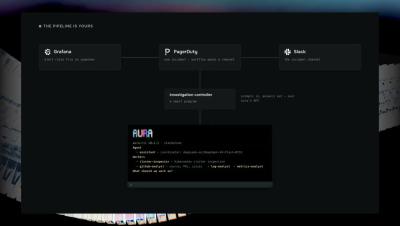
AURA runs as a standalone service and knows nothing about Slack. A separate bridge streams events off its API, which is what makes the chat tool swappable. This is the implementation behind the automated PagerDuty investigation demo. Jeff Vogt walks the whole path an incident takes: a Grafana alert fires PagerDuty, PagerDuty opens a Slack channel and sends a webhook, and a service called AURA Bridge picks it up and calls AURA's API with an investigation prompt.

Tech Talk #14 - Skill issue: A guide to Using AI skills with VictoriaMetrics

An engineer in an incident does not have a metrics problem, a logs problem and a traces problem. They have one question, and answering it today means opening three interfaces and retyping the same timestamp, service name and tenant into each one.

Canonical joins the Open Secure AI Alliance

Canonical is now part of the Open Secure AI Alliance, announced by NVIDIA with partners across cloud computing, cybersecurity, enterprise software, open source foundations, and AI research. The alliance aims to develop and share open technologies, techniques, and tools to safeguard software and agents in the age of AI.

AI harnesses for telco autonomous networks

Across the global landscape, telecommunications operators have already deployed machine learning for predictive maintenance, customer care chatbots, and anomaly detection. However, as the industry transitions toward Autonomous Networks Level 4 (AN L4), where networks can make intent-driven, predictive decisions and perform closed-loop management with minimal human intervention, a fundamental architectural challenge has emerged.

No more manual invoicing: How ManageEngine MSP Central automates usage-based billing

ManageEngine MSP Central's billing capability, powered by Zoho Billing, is officially live—and the headline feature is automated usage-based billing. No more pulling usage numbers manually, matching them to invoices, and updating everything by hand every month. Here's what changes: Customer data syncs automatically from MSP Central to Zoho Billing—no duplicate client records. Every service you deliver, including endpoint management, ITSM, and infrastructure monitoring, becomes billable in Zoho Billing without manual setup. Set up subscriptions per client, per service—one client can run multiple subscriptions at once.

Introducing APEX: Adversarial Pattern Extraction and Correlation

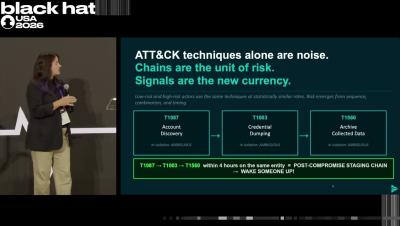
In this Black Hat talk, Nicole Beckwith introduces APEX (Adversarial Pattern Extraction and Correlation), a detection framework—not a Cribl product—that clusters TTP-based signals around entities to support behavioral detection. It is intended for security practitioners, SOC and detection teams, and threat hunters who want to learn how to use raw telemetry or OCSF data, TTP chaining, time windows, criticality, and cross-correlation to detect behavior beyond static indicators and rule-count coverage.