Operations | Monitoring | ITSM | DevOps | Cloud

How to Reduce Vendor Sprawl: A Practical Guide for IT Teams

To reduce vendor sprawl, start with inventorying what your tools do, who depends on them, and where their capabilities overlap. Then decide which tools to retain, connect, or replace. When going away from tool sprawl, you need to aim for a smaller toolset that your team can manage while still supporting the work your organization needs. This guide walks through spotting unnecessary fragmentation, assessing whether consolidating makes sense or not, and transitioning to it.

UPS Monitoring for Data Centers That Cannot Afford an Unplanned Stop

How many minutes of battery runtime are left in the unit protecting your primary rack right now? Most monitoring deployments can answer a question like that for every switch, server and virtual machine in the building. Ask about power and the dashboard goes quiet. Backup power tends to fall between two owners. Facilities buys the hardware and books the service visits, while IT owns everything plugged into it.

Digital Signature vs Electronic Signature and When ITSM Approvals Need Each

Would a single click on Approve in your service desk satisfy an auditor reviewing a high-risk change, a purchase order, or a vendor contract? Often the answer only becomes clear when someone requests a signed copy and the ticket has nothing to show. Much of this traces back to terminology. Many organizations treat electronic signatures, digital signatures, and approvals as interchangeable, and ITSM tools tend to call every sign-off an approval.

Moving Alert and Email-to-Ticket Mail off SMTP AUTH to Microsoft Graph API

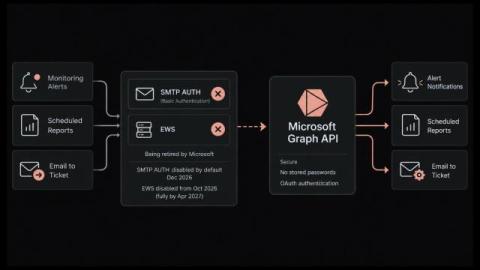
Every monitoring alert, scheduled report, and email to ticket conversion in your stack depends on a mailbox. Most monitoring and helpdesk management tools still reach that mailbox the old way. They log in with a username and password over SMTP or EWS. Exchange Online is closing both doors on a published schedule. The tools that fail will fail silently. In this blog, you will: By the end, you can run the change on a weekday afternoon and know nothing went quiet.

It takes a hacker 48 hours to exploit a vulnerability. Why does it take 43 days to patch it?

It is not always possible to patch vulnerabilities as quickly as hackers exploit them, but recent figures show just how much this gap has widened. FortiGuard Labs estimates that the time between the disclosure of a critical vulnerability and its active exploitation has dropped sharply to between 24 and 48 hours. By contrast, Verizon’s 2026 Data Breach Investigations Report shows that organizations take a median of 43 days to complete vulnerability remediation.

macOS Patch Management for Mixed Windows and Mac Fleets

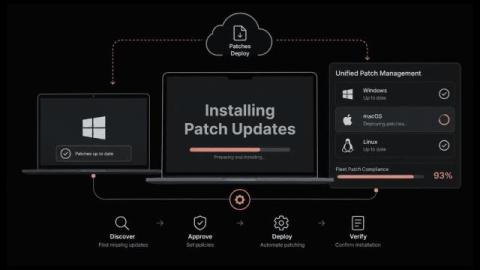
How many Macs in your environment are running an OS build that your patch compliance report has never counted? In most mixed Windows and Mac deployments, the Windows side is managed by policy and the Mac side is managed by hope. Designers, executives, and engineering leads install updates when a notification interrupts them, and otherwise dismiss the prompt for months.

How Traceroute Works and How to Read Its Output During an Outage

Users report that an internal application has gone slow, the server dashboards look normal, and the network group says nothing changed on their side. So where between the user and the application does the time actually go? Much of that answer comes from traceroute. The command lists every router a packet crosses on the way to its destination, with a timing figure set against each one. Arguments about ownership then come down to a single device on a single route.

ISO 20000 Certification: Prerequisites, Process, and Cost

ISO 20000 certification means two different things depending on who is asking. One is an audit of your organization against ISO 20000. The other is an exam that one person sits. Search results mix the two together, and teams lose weeks to it. A service desk manager hunting a company certificate lands on a training catalog. They book a course nobody needed. In this blog, you will: You will finish able to scope the project and brief a certification body.

How to Fix DNS Server Not Responding Errors and Keep Users Online

Has your service desk ever filled with "the internet is down" tickets while every switch, firewall and uplink is reporting normal? The connection is usually fine. What has failed is name resolution, and the message your users see says the DNS server is not responding.

10 Top Network Traffic Analysis Tools for Faster Troubleshooting and Capacity Planning

A request to upgrade a saturated circuit is easy to raise and hard to defend. The interface graph proves the link is full. It says nothing about which application, host or conversation filled it, so the spend gets approved on assumption instead of evidence. The same missing detail turns up everywhere else. Incidents run long because the cause is guessed at, capacity planning rests on estimates, and security questions arrive weeks after the traffic record expired.

How to Manage Shadow IT in 2026: Detection, Policy And Control

Shadow IT is any hardware, software or IT resource running inside your organization that the IT department never approved, never configured and, in most cases, does not know exists. It covers the file sharing account someone opened with a departmental card, the personal laptop plugged into the office network, and the AI assistant installed on a work machine last Tuesday. None of it is necessarily malicious, and all of it sits outside every control you have.

9 Best Log Management Tools and What They Cost

Most log management tools bill you on log ingestion, the volume of data you send them. That works until your log volume doubles, and the invoice doubles with it. The best log management tools let you control what gets indexed and kept, so growth stops being a budget problem. In this blog, you will see: By the end you will know which fits your volume. Log management is the full lifecycle of your log data, from the moment it is collected to the moment it is deleted.

ISO 20000 in ITSM: What the Standard Actually Requires From Your Service Desk

Certification against ISO 20000 puts your service desk under audit. That audit runs on what your team wrote down at the time. The standard does not care how your team describes its process. It does not care which ITIL 4 practices you adopted. It cares what your records show, so auditors spend their time in your tickets, approvals, and review minutes. In this blog, you will: You will finish knowing which of your records would survive an audit.

Almaden, Inc. Announces General Availability of CIQ Cloud, an Operational Visibility Platform for MSPs and IT Teams

Almaden, Inc. today announced the general availability of CIQ Cloud, its Operational Visibility platform designed to help Managed Service Providers (MSPs) and internal IT teams monitor, understand, govern and optimize increasingly complex cloud and SaaS environments. Modern organizations rely on Microsoft 365, Google Workspace, cloud infrastructure, SaaS applications, identity services, security platforms, DNS and a rapidly growing range of AI technologies.

IBM Warranty Check: How to do it And How to Automate it

An IBM warranty check sounds like a ten second task: type in the serial number, read the expiration date. In practice, a lot of people hit a sign in screen or a result telling them the machine cannot be found. The reason is rarely the serial number itself. Most hardware that people still call IBM is serviced by Lenovo today, so half of these lookups happen on the wrong website.

MSP Ticketing System: How to Evaluate and Choose the Right Platform

Most managed service providers do not replace their ticketing tool because ticket volume got too high. They replace it because a client asked for a report the tool could not produce. That moment usually arrives between the third and tenth client. The shared inbox and the general help desk that carried you this far stop holding the accounts apart. Per-client reporting is usually the first thing to give way. An MSP ticketing system takes support requests from every client you serve.

The Essential Eight: Patching Applications and Operating Systems at Maturity Level Two

Why do so many patching programs pass every internal check and still come back from an Essential Eight assessment rated at Maturity Level One? The answer is rarely speed. Teams that miss the mark are usually patching their servers, browsers, and office suites on schedule, then losing the rating on the fifty applications nobody put on a list. Maturity Level Two is where the Essential Eight stops asking how fast you patch and starts asking how much you can see.

PCI DSS Requirement 10: Logging and Monitoring in v4.0.1

Version 4.0 renumbered PCI DSS Requirement 10 from end to end, and the Council retired v3.2.1 on 31 March 2024. Sub-requirement numbers written before then mostly point somewhere else now. Four more Requirement 10 rules changed status on 31 March 2025, automated log review among them. Checking your numbering against v4.0.1 costs an afternoon and saves a finding. In this blog, you will: PCI DSS Requirement 10 covers audit logging and monitoring across the cardholder data environment.

ITSM for Healthcare: IT Service Management in Hospitals and Health Systems

How long does a nurse stand at a workstation waiting for a record to load before the ward gives up and reaches for paper? In most hospitals nobody measures that number, and the ticket that reaches IT describes a symptom instead of a cause. Hospital IT support runs on a different clock from corporate IT. There is no quiet Sunday night and no safe window for maintenance.

Log Filtering: How to Cut Log Ingest Volume Without Losing Evidence

Every log estate reaches a point where volume grows faster than the value inside it. The usual response is to find the biggest source and drop it. Cutting volume is the easy part. Cutting the right half takes judgment. Log filtering is only one of four options for an expensive source, and the other three matter just as much. In this blog, you will: By the end you can defend every rule you write, including the ones that keep data. A volume cut fails in two directions.

Agent vs Agentless Monitoring and How to Decide What Goes Where

Why does half the infrastructure end up returning no monitoring data? The standard plan is to install collection software on everything, which moves quickly across servers and stops dead at the first device running closed firmware. Storage arrays, firewalls, and switches will never accept an install, and the rollout stalls there. That plan usually gets set once for the whole environment, with a single collection model applied to hardware it was never suited for.

Help Desk Software for Schools: Managing IT Support Across Campuses

How many support requests reach school IT staff each week without ever becoming a ticket? A teacher stops a technician in the corridor about a projector that will not connect. An office administrator sends a direct email about a locked account, and a student tells the librarian their laptop stopped charging during second period. Help desk software for schools collects those requests into one queue, routes them by site and category, and keeps a record of what was done.

10 Top Website Monitoring Tools for Uptime, Page Speed and Real User Data

Your uptime tool reports the site as available all month. Support reports something else, because customers in one region spent the morning unable to complete a checkout. Both records are accurate, and that is the problem. An external check confirms the page answered. It cannot tell you that the answer took nine seconds for everyone routed through one CDN edge, or what caused the delay.

ITSM Maturity Model: The 5 Levels And Where AI Fits at Each One

An ITSM maturity model is a practical framework for measuring where your Service Management stands across people, processes, technology, and governance, then turning that baseline into a prioritized improvement plan. Most models describe five levels — from ad hoc to optimized — with clear characteristics and outcomes at each stage. This guide explains the levels, how to assess your current state, how to map capabilities to ITIL 4 practices, and actionable steps to get started.

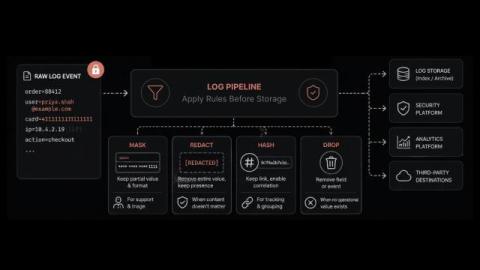
PII Redaction in Logs: Mask, Redact, Hash, or Drop?

Sensitive values reach your logs without anyone deciding they should. A debug line prints a whole request object. An error message carries the query string. A customer email address is suddenly stored in three systems. PII redaction in logs then gets treated as one setting to switch on. In practice it covers four separate treatments. The value is already inside the message before log ingestion finishes. In this blog, you will: By the end you can write a rule for each field and defend it.

Log Processing: What Happens to a Log Line Before You Can Search It

A log line arrives as plain text and leaves as a record you can query. Six steps sit between those two states. Each one adds something useful, and each one costs you time, CPU, or storage. Most teams never look at that chain until a search comes back empty. Here is what log processing does to an event, step by step: By the end you can look at your own chain. You will know what each step buys you. Six steps turn a raw log line into a searchable record.

How Logicalis Scaled Security Operations with Autonomous Endpoint Management

Learn how Logicalis, a global technology service provider, partnered with Ivanti to transform their IT operations. Discover how they leveraged automation and Ivanti Neurons to streamline workflows, reduce manual intervention, and deliver exceptional service at scale. Key Highlights: How Logicalis simplified complex global IT environments. The role of automation in improving service delivery and response times.

How NIST Compliance Turns Observability Data Into Audit Evidence

Can you prove, on demand, which production systems were under continuous monitoring last quarter? Buyers, auditors, and insurers all ask a version of that question, and the answer decides contracts as often as audit findings. NIST compliance means aligning security controls and operations with standards from the National Institute of Standards and Technology, then holding evidence that the alignment stayed continuous. The frameworks are precise about outcomes and quiet about mechanics.

Best Storage Monitoring Software: 10 Tools Compared

Storage rarely fails loudly. A pool fills. Latency climbs on one LUN. The first to notice is a user whose application timed out. The best storage monitoring software catches it earlier. It watches capacity, IOPS, latency and drive health across your arrays, which is what storage resource monitoring is for. In this blog, you will see: By the end you will know which one fits. Storage monitoring software tracks the health, capacity and performance of your IT storage.

The invisible challenge that kills IT projects

The verdict on enterprise AI is starting to sound familiar: It didn't deliver. But the real question is: Did we ever define what deliver meant in the first place? If success was never tied to measurable business outcomes, AI was always going to fall short, no matter how capable the technology was. Before the next budget cycle dismisses AI, ask whether the problem is the technology or the lack of clear success metrics.

InvGate Updates: AI Hub Reports, VSA in Slack, Asset Leasing and more

New updates are now available across InvGate Service Management and InvGate Asset Management. Watch the video for a quick look at our latest additions, including the AI Hub Reports to measure your Virtual Service Agent’s performance and the ability to interact with the Virtual Service Agent directly within Slack. We’ve also introduced an asset-based lease cost model for hardware contracts and added granular control over location and people access permissions by role.