Operations | Monitoring | ITSM | DevOps | Cloud

The latest News and Information on Log Management, Log Analytics and related technologies.

Loop Engineering Guardrails for iGaming with Claude Code and CX CLI

Tuning guardrails can take time. To accelerate this, we combined the power of Claude Code, Coralogix Telemetry and the CX CLI, to build a loop that iterates on guardrails. To test our loop, we built a fictional chat interface for an iGaming operator, that took bets, gave odds on markets and more, but with a catch: this agent was not permitted to make predictions about where the market was going. With our goal in place, we got to work designing our loop.
Introducing APEX: Adversarial Pattern Extraction and Correlation

In this Black Hat talk, Nicole Beckwith introduces APEX (Adversarial Pattern Extraction and Correlation), a detection framework—not a Cribl product—that clusters TTP-based signals around entities to support behavioral detection. It is intended for security practitioners, SOC and detection teams, and threat hunters who want to learn how to use raw telemetry or OCSF data, TTP chaining, time windows, criticality, and cross-correlation to detect behavior beyond static indicators and rule-count coverage.

Mobot levels up: Build incident response playbooks with natural language

We’ve recently shown how Mobot, Sumo Logic’s AI assistant, has evolved from a search assistant into a true thinking partner, introducing natural language to log analysis and monitors. Today, we’re bringing that same conversational reasoning to one of the most powerful parts of the platform: playbooks in Automation Service. Historically, playbook authoring has been a highly manual process that required deep organizational and Sumo Logic platform knowledge.

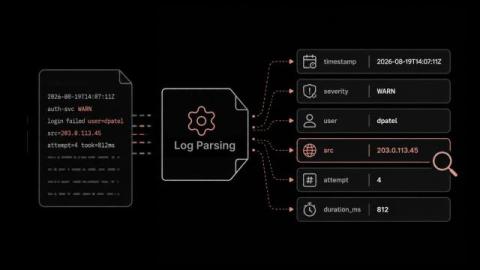
Log Parsing: How Raw Logs Become Searchable Fields

A log file full of raw text is close to useless when an incident is running. You can grep it. What you cannot do is ask how many failed logins came from one address in the last ten minutes. That is usually the question in front of you. Log parsing closes that gap, and a log parser is the software that does the work. In this blog, you will see: Log parsing is the process of reading a raw log line and extracting its values into named, structured fields.

AI SRE Agent Audits Runbook Coverage and Opens the PRs: AURA

3 a.m., the pager fires, and the runbook describes a service that shipped three versions ago. Ask the agent what the cluster actually has instead. Runbooks go stale because clusters change faster than documentation does. Every deploy, every new service, every renamed alert widens the gap between what is running and what is written down.

Zero To Logs - Getting Graylog Up and Running in Under an Hour Webinar

Getting Graylog up and running does not have to take hours of configuration work. In this session, Graylog Director of Technical Marketing Jeff Darrington walks through a complete installation using Docker Compose, taking you from a blank environment to a fully functioning log management platform with live data ingestion in under an hour.